sentinel
Exactly-Once Log …
Summarization and Current Limitations Firewall, DNS and proxy logs produce millions of events a day. Keeping them all in the Sentinel analytics tier is expensive; keeping them only in the data lake means no analytics rules can run on them. Summarization is the middle ground: the raw events stay in …
Summarization with Data …
Exactly-Once Log Summaries with Sentinel data lake and Fabric Firewall, DNS and proxy logs produce millions of events a day. Keeping them all in Sentinel analytics tier is expensive; keeping them only in the data lake means no analytics rules on them. Summarization is the middle ground: the raw …
Auditing Sentinel Queries …
Who Read What? SOC analysts run hundreds of KQL queries against Microsoft Sentinel every day, and the data they read is anything but harmless: passwords leaked into command lines, email subjects, sometimes card numbers in custom tables. With an external SOC - or an AI agent querying your workspace - …
Sentinel Data Lake 2.0
On 23 September 2026, Microsoft changed how new customers get the Microsoft Sentinel data lake experience. Most posts since then focus on the simpler onboarding, but the update also changes which features you get and how the APIs behave. The documentation does not cover all of it, so I tested it in …
Sentinel Protected Tables
Microsoft Sentinel workspaces tend to hold tables that were never meant for a wide audience - HR investigation logs, insider threat cases, AI prompt histories, sign-in records full of PII - or security data in general. But cloud admins, MSSP operators, and other high-privilege users can read every …
Data Processing Cost …
Data Collection Rules (DCRs) let you filter and transform logs before they land in your Log Analytics workspace. This is great for reducing ingestion volume and cost — but the transformation itself can carry a data processing charge depending on the destination table plan and whether Microsoft …
Patching the Sentinel MCP …
MCP servers are now the default way to connect AI to real systems, tools and data. In SOC scenarios, they are used to pull logs, run hunts, and automate response steps. It feels clean and simple: you ask the model, it calls the tool, you get what you were looking for. Reality is messier. MCP servers …
Logs to ADX from all your …
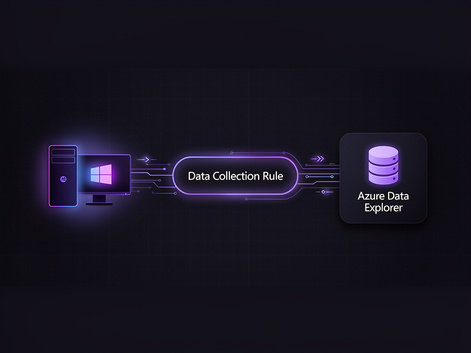
In a previous post, I explored how Azure Monitor Agent (AMA) could turn Event Hubs into a reliable, scalable backbone for your logging infrastructure, effortlessly pulling logs from Azure VMs and routing them to Event Hubs or Storage Accounts. But here comes the bad news: Microsoft just announced …